01 —Board & Executive Briefings
Interactive AI and cyber risk briefings for boards and executive teams, facilitated by former Group CISOs.
Advisory led by former Group CISOs — Sydney, working globally
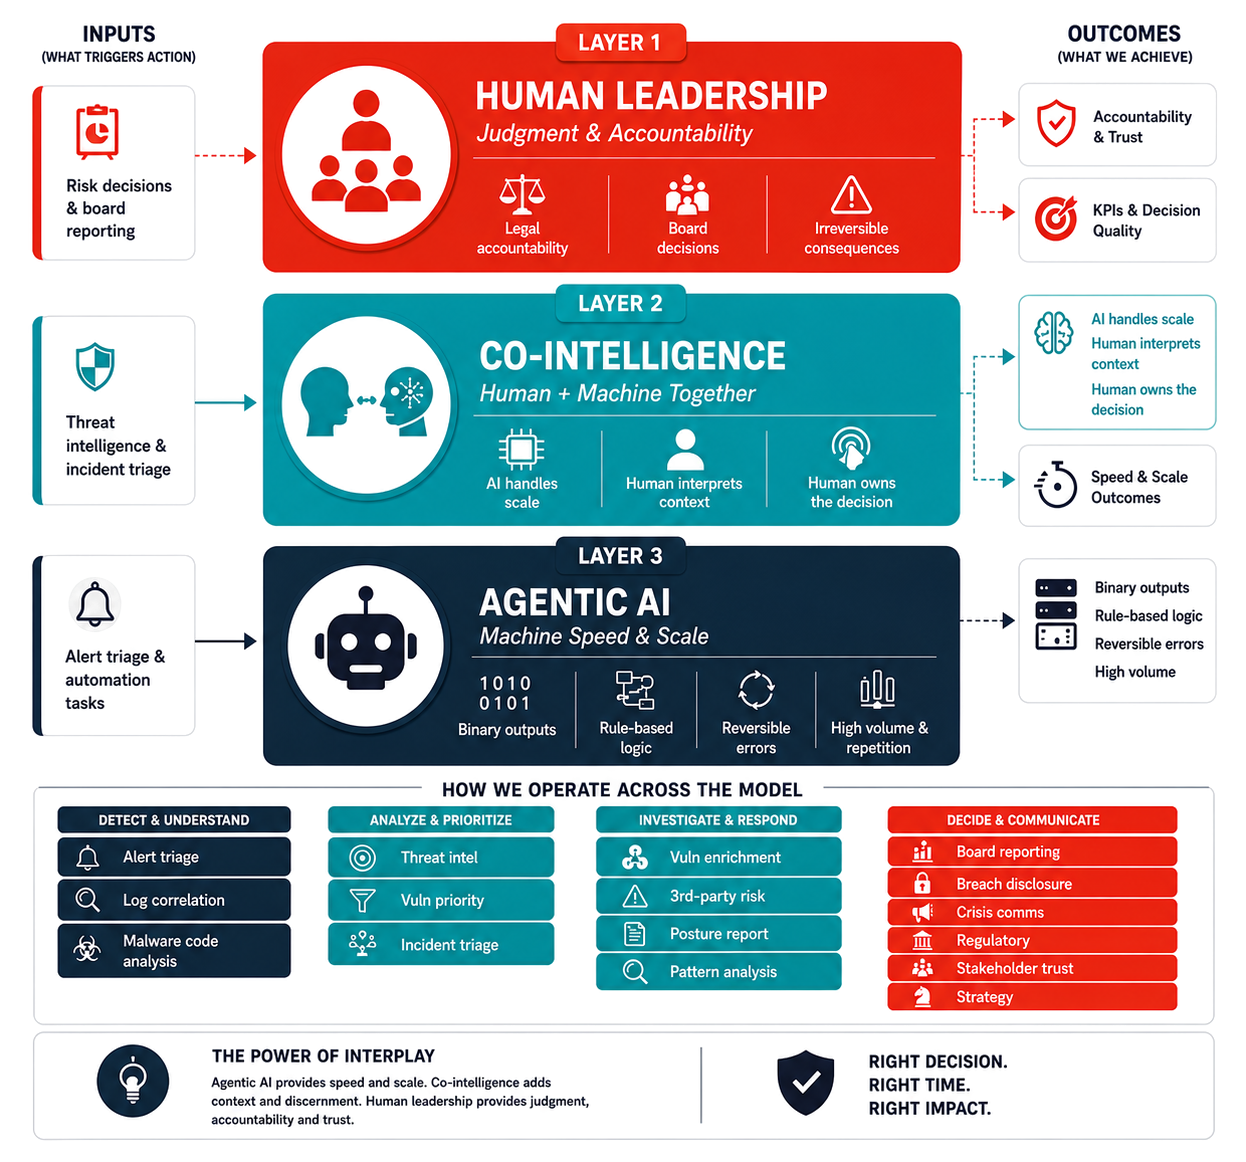
Cyber Resilience helps organisations build modern cyber security capability through experienced senior cyber security professionals, enhanced by AI driven approaches that accelerate delivery and improve outcomes. We support organisations facing increasing cyber risks, regulatory obligations, and the challenges of adopting AI, particularly where they lack dedicated senior cyber security leadership.
Our practical, real world advice and solutions reduce cyber risk while enabling organisations to embrace AI securely and confidently, strengthening resilience against an increasingly sophisticated threat landscape. We call this the Cyber Resilience & AI Interplay method.
The outcomes of this approach
From a single boardroom briefing through to a fractional CISO who stays with you, each engagement is sized to what you actually need — and hands capability back to your team.
Interactive AI and cyber risk briefings for boards and executive teams, facilitated by former Group CISOs.
Determine the strength of existing defences, understand where AI creates new exposure, and agree your current maturity on a scale of one to five.
A business centred strategy covering cyber and AI risk, so you reach target maturity cost effectively and can adopt AI with confidence.
Agile governance, AI oversight, advanced technology, lean process and skilled people — the capability to reach your target maturity and risk profile.
Four things clients tell us they do not get elsewhere.
Delivered by experienced senior cyber security professionals, for organisations facing significant risk, regulatory obligations or the challenge of adopting AI safely — particularly those without a full-time senior cyber executive. Practical, real-world advice that reduces risk while letting the business move.
Whilst traditional approaches start with a predefined set of controls and build frameworks on generic best practice, our approach starts with your business priorities, target markets, operating environment and value chain — including where AI creates advantage and where it creates exposure. That is what earns wider enterprise buy-in for cyber and AI initiatives.
Most security models are needlessly complex. Effectiveness requires focus. A strategy centred on what your customers genuinely value eliminates waste, so you reduce risk cost effectively and adopt AI without the governance becoming a brake.
To help you rapidly build and maintain capability, we offer flexible service models tailored to your needs. Our virtual and fractional CISO models provide executive-level cyber and AI risk expertise at a fraction of the cost of a full-time CISO, scaling up or down as your requirements change.
Practical, field-tested guides for the people now accountable for cyber and AI risk — written by former Group CISOs who have sat in the chair and reported to the board.
For CISOs, CIOs & boards
Six pillars for governing AI risk without slowing AI adoption — redesigning the security function for the AI era, standing up governance that actually decides, assuring AI systems, protecting high-value AI assets and agents, and securing the AI supply chain.
Get the playbook→
For new & aspiring CISOs
The SUPER leadership framework and a five-phase action plan for newly appointed security leaders. Understand the business before you transform it, clarify your mandate, build trust before you need it, and know what to put in your day-100 executive report.
Get the playbook→
For CISOs & security leaders
Ten recommendations for building a high-value, business-aligned cyber resilience strategy — from diagnostic and stakeholder buy-in, through protecting the crown jewels and meeting regulatory obligations, to agreeing a target state and delivering quick wins.
Get the playbook→
Whether you need a board briefing, a strategy you can defend, or a CISO for the days you actually need one.